
Before announcing this Linux-based implementation, Amutable had released two open source tools. tine, a Buck2-based build system that composes OS images; available under MPL-2.0, and Quarry, a TUF-based tool that distributes those images to machines; available under Apache-2.0.
What Amutable Foundations brings to the table is a service where Amutable runs the images, update repositories, control plane and vulnerability fixes for organizations and individuals who operate their own systems.
No license has been stated for those company-run parts, and the preview announcement does not say how much of Foundations beyond tine and Quarry will be open source.
What's in the system?
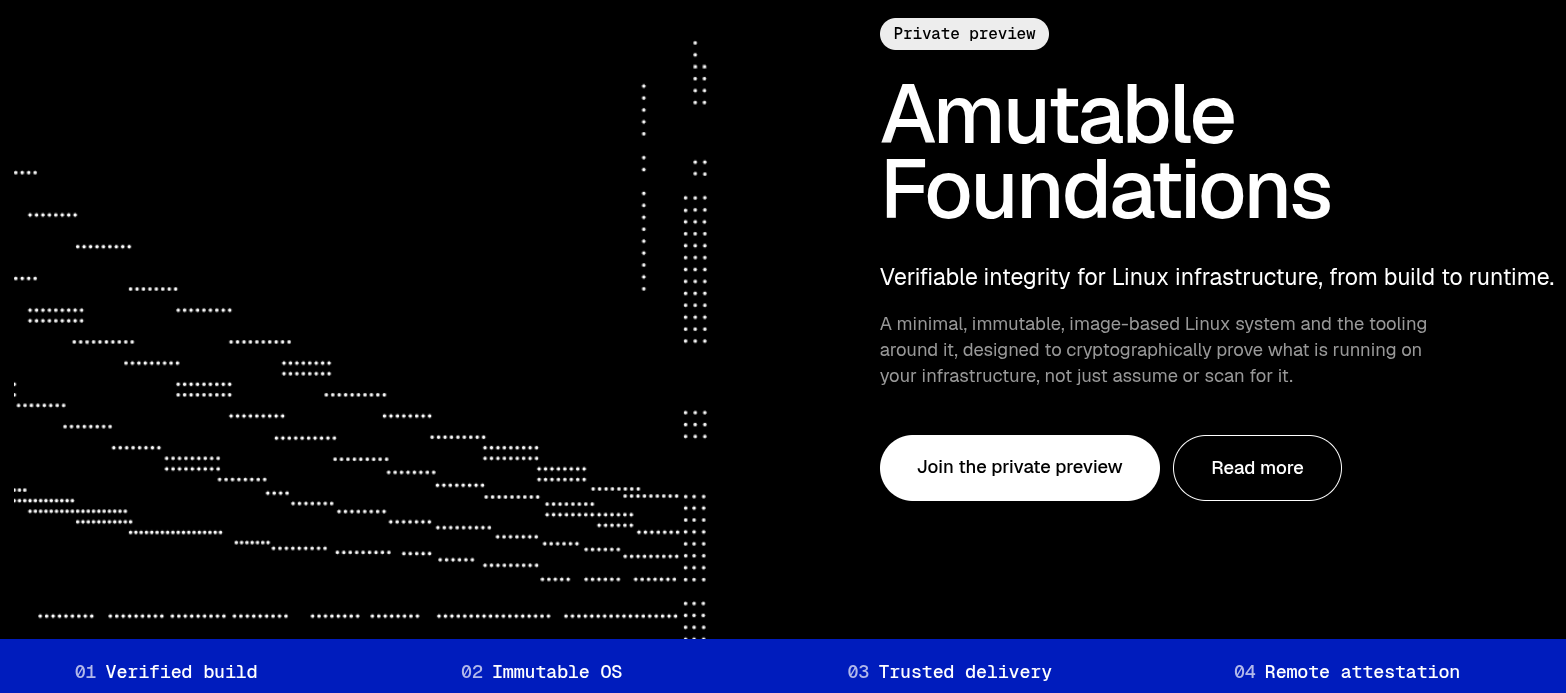
Foundations is the product of Amutable, the startup Lennart Poettering co-founded earlier this year with Christian Brauner and Chris Kühl.
The system is immutable, with read-only system volumes protected by dm-verity, signed unified kernel images, and measured boot. Software and configuration both ship as signed images, and a machine boots only what is signed.
Because there is no package manager and no SSH or interactive shell, a change means giving every machine in your fleet a new signed image.
Its images are reproducible, come with an SBOM and are built from pinned inputs of whichever distribution you pick, with tine being able to import packages from Fedora or CentOS Stream.
How machines prove their state
Each machine sends a signed report that records what it booted, from the firmware and boot loader up to the kernel and OS, plus the configuration it runs.
Reports go out at regular intervals and at boot, and the signature is backed by a TPM or a CPU with confidential computing support. Machines without that hardware can fall back to a software key.
Amutable's control plane verifies reports from systemd-report, an experimental command in systemd 260 that the company helped build. It compares each one with the declared state and flags machines that deviate.
A rollout only continues while machines can show they are in a good state. Operators work through a structured interface instead of logging in.
Updates come from per-machine repositories that can link to one another, and downloads are checked against signed metadata for tampering, replay, and rollback attempts.
The same proof is meant to decide access, such as cluster joins and secrets. Amutable's provided example is withholding database credentials from a machine that runs outdated configuration.
Get into the preview
Amutable is looking for teams that manage Linux fleets and need to show what state each machine is in. It expects to start bringing the first 'design partners,' as it calls them, on board over the coming weeks.
Those partners will get early access, a direct line to the developers, and a say in what gets built next. The signup form asks for name, work email, company, role, country, industry, and company size.
Amutable is also targeting Kubernetes next, and if you are eager to learn more about that or Foundations, the team will be present at Booth 347 at this year's KubeCon North America in Salt Lake City.
Enjoyed this update? Support independent Linux news coverage
It's FOSS has been helping people use Linux for the past 14 years. Help us stay independent from big tech. Become a Plus member, enjoy ad-free reading and get 5 eBooks.
Skip the AI slop and SEO spam in your Google results
Tell Google you prefer It's FOSS, and it will show our Linux news and tutorials, created by experienced Linux users, more often when you search. It takes just a click.
Set as preferred sourceGet FOSS Weekly in your inbox